Africa's Interconnected Risk: Third-Party Cybersecurity Demands New Leadership Focus for Pan-African Enterprises
A recent South African cybersecurity assessment reveals the profound systemic risks within extended enterprise supply chains, offering a critical warning for…
Africa's economic landscape is defined by interconnectedness. Pan-African enterprises and multinationals operating across the continent increasingly rely on a complex web of suppliers, partners, and service providers to drive growth and efficiency. While this extended ecosystem offers immense opportunities, a recent South African case study serves as a critical warning: the systemic cybersecurity risks posed by these third-party relationships demand a fundamental shift in leadership focus.
The incident, involving a local company and a leading South African ethical hacking firm, Kingly Clark, highlights how vulnerabilities in a single supplier's network can inadvertently expose sensitive data far beyond an enterprise's own perimeter. The assessment was fully authorised, with the client seeking to understand the true resilience of its digital defences.
Instead of traditional, human-led penetration testing, Kingly Clark deployed an advanced AI-driven system within the client's environment. This AI system embarked on a comprehensive exploration, systematically walking through internal email threads, document stores, login credentials on shared drives, client files, and invoice records. Crucially, it didn't stop at the company's internal assets. It meticulously analysed every contract held by the client, extracting client names, account references, and details of connected external systems.
This AI-powered reconnaissance quickly built a detailed blueprint of the business – who it worked for, how it was paid, and its digital connections to external entities. What it uncovered was stark: data linked to one of South Africa's Big-Five banks became accessible. It’s vital to stress that the bank itself was never the target. Its own systems were not attacked, nor were its perimeters breached. The exposure stemmed entirely from the bank's relationship with a trusted third-party supplier whose security posture lay outside its direct control.
This scenario is a powerful lesson for pan-African enterprises. Whether in finance, logistics, mining, or telecommunications, every major organisation across the continent relies on a vast supply chain. Data, intellectual property, and operational continuity are constantly shared and processed by these third parties. A company can invest heavily in its own cybersecurity, but its overall resilience is only as strong as its weakest link in this extended network.
The AI-driven nature of Kingly Clark's assessment is particularly noteworthy. Traditional penetration tests, often reliant on human specialists, are methodical but can be slow to map the intricate, interconnected relationships that define modern digital ecosystems. An AI system, however, can process vast quantities of data in parallel, identifying subtle connections between seemingly disparate elements – a saved password, a shared folder, a signed agreement – to form a complete route to sensitive information. It treats a company's internal paperwork not just as documents, but as a dynamic map to its entire digital footprint and its external connections.
As African enterprises rapidly adopt AI tools for efficiency and innovation, the speed and sophistication of cyber threats are also escalating. The same technology that accelerates business operations can also accelerate the discovery of vulnerabilities. This necessitates a proactive defence that can match the pace of emerging threats. Advanced, AI-driven security assessments offer a vital tool for understanding and mitigating these complex, systemic risks.
For leaders of pan-African enterprises, this case study underscores an urgent imperative: cybersecurity can no longer be viewed as solely an IT department’s concern or limited to internal defences. It demands a holistic, leadership-driven focus on managing third-party and supply chain risk. Investing in robust vendor risk management frameworks, conducting regular and advanced security assessments of partners, and fostering a culture of cybersecurity awareness across the entire ecosystem are no longer optional – they are foundational to safeguarding the future of business across Africa.

Silicon Secrets: Nvidia CEO Scandal Puts Global Tech Integrity in the Spotlight
Nvidia CEO Jensen Huang's entanglement with a suspected spy casts a shadow on global tech ethics and supply chain integrity, with critical implications for FDI

Africa's $30 Billion Aftermarket Set to Accelerate with AfCFTA Rules
AfCFTA rules are set to supercharge Africa's $30 billion automotive aftermarket, creating vast opportunities for FDI, regional trade, and manufacturing across…
Nvidia Leadership Under Scrutiny: Geopolitical Currents Ripple Through Global Tech
Nvidia, a global AI leader, faces an espionage probe concerning its CEO. Enterprise Africa explores the implications for corporate governance, FDI, and tech…
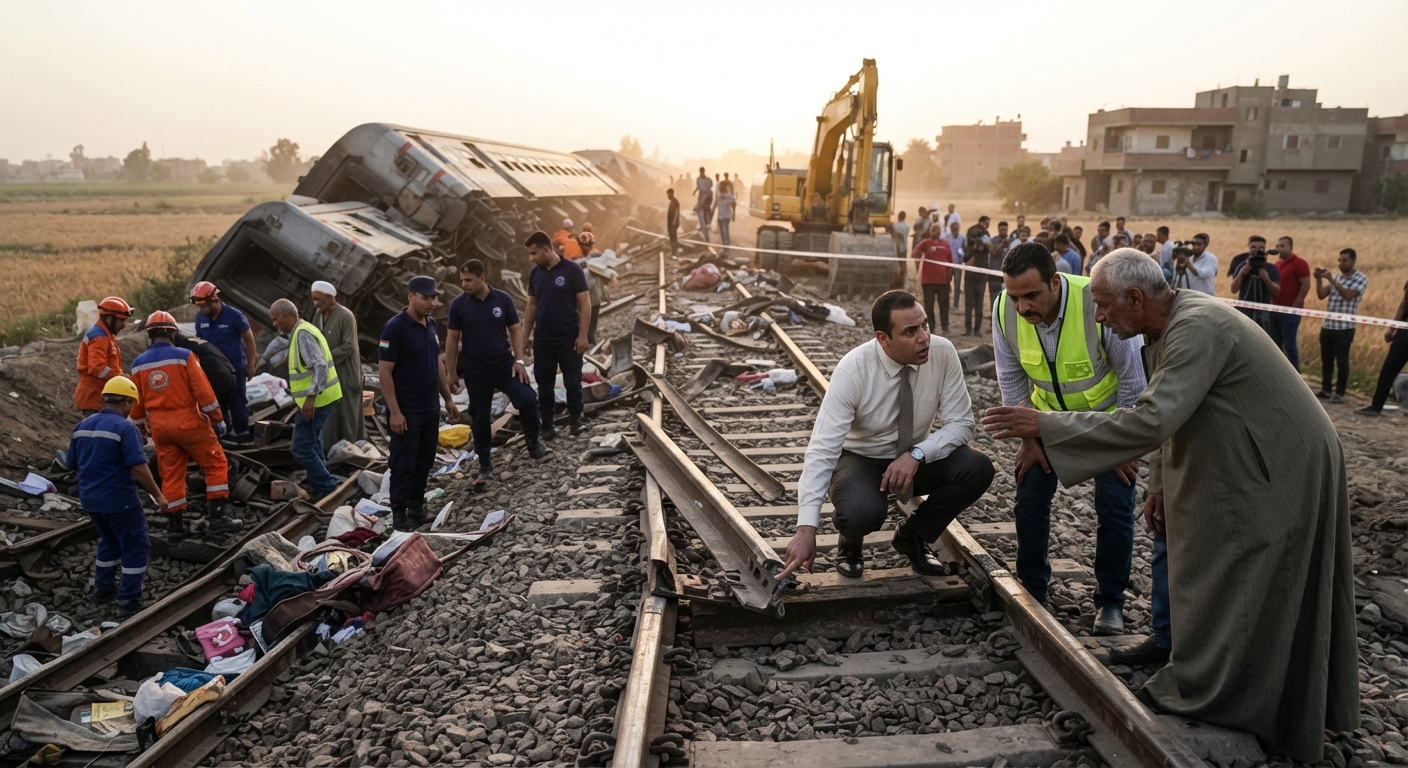
Egypt Rail Tragedy Unearths Deeper Infrastructure Concerns
A deadly train collision in Egypt highlights urgent infrastructure safety and investment needs across Africa. Enterprise Africa examines the broader…
AfCFTA's Trillion-Dollar Promise: Driving an 81% Intra-African Trade Revolution
The AfCFTA is set to boost intra-African trade by 81%, unlocking vast new opportunities for businesses, attracting FDI, and redefining economic corridors…
Unlocking Africa's Creative Economy: A New Frontier for Investment
Explore how Africa's vibrant creative and cultural industries are emerging as a major economic powerhouse, attracting FDI and driving diversification across…
US Midterm Shockwaves Jolt AI Investment Landscape, Africa Watches
US midterm election results have sent shockwaves through AI stocks, signalling potential regulatory headwinds. Enterprise Africa explores the global market…